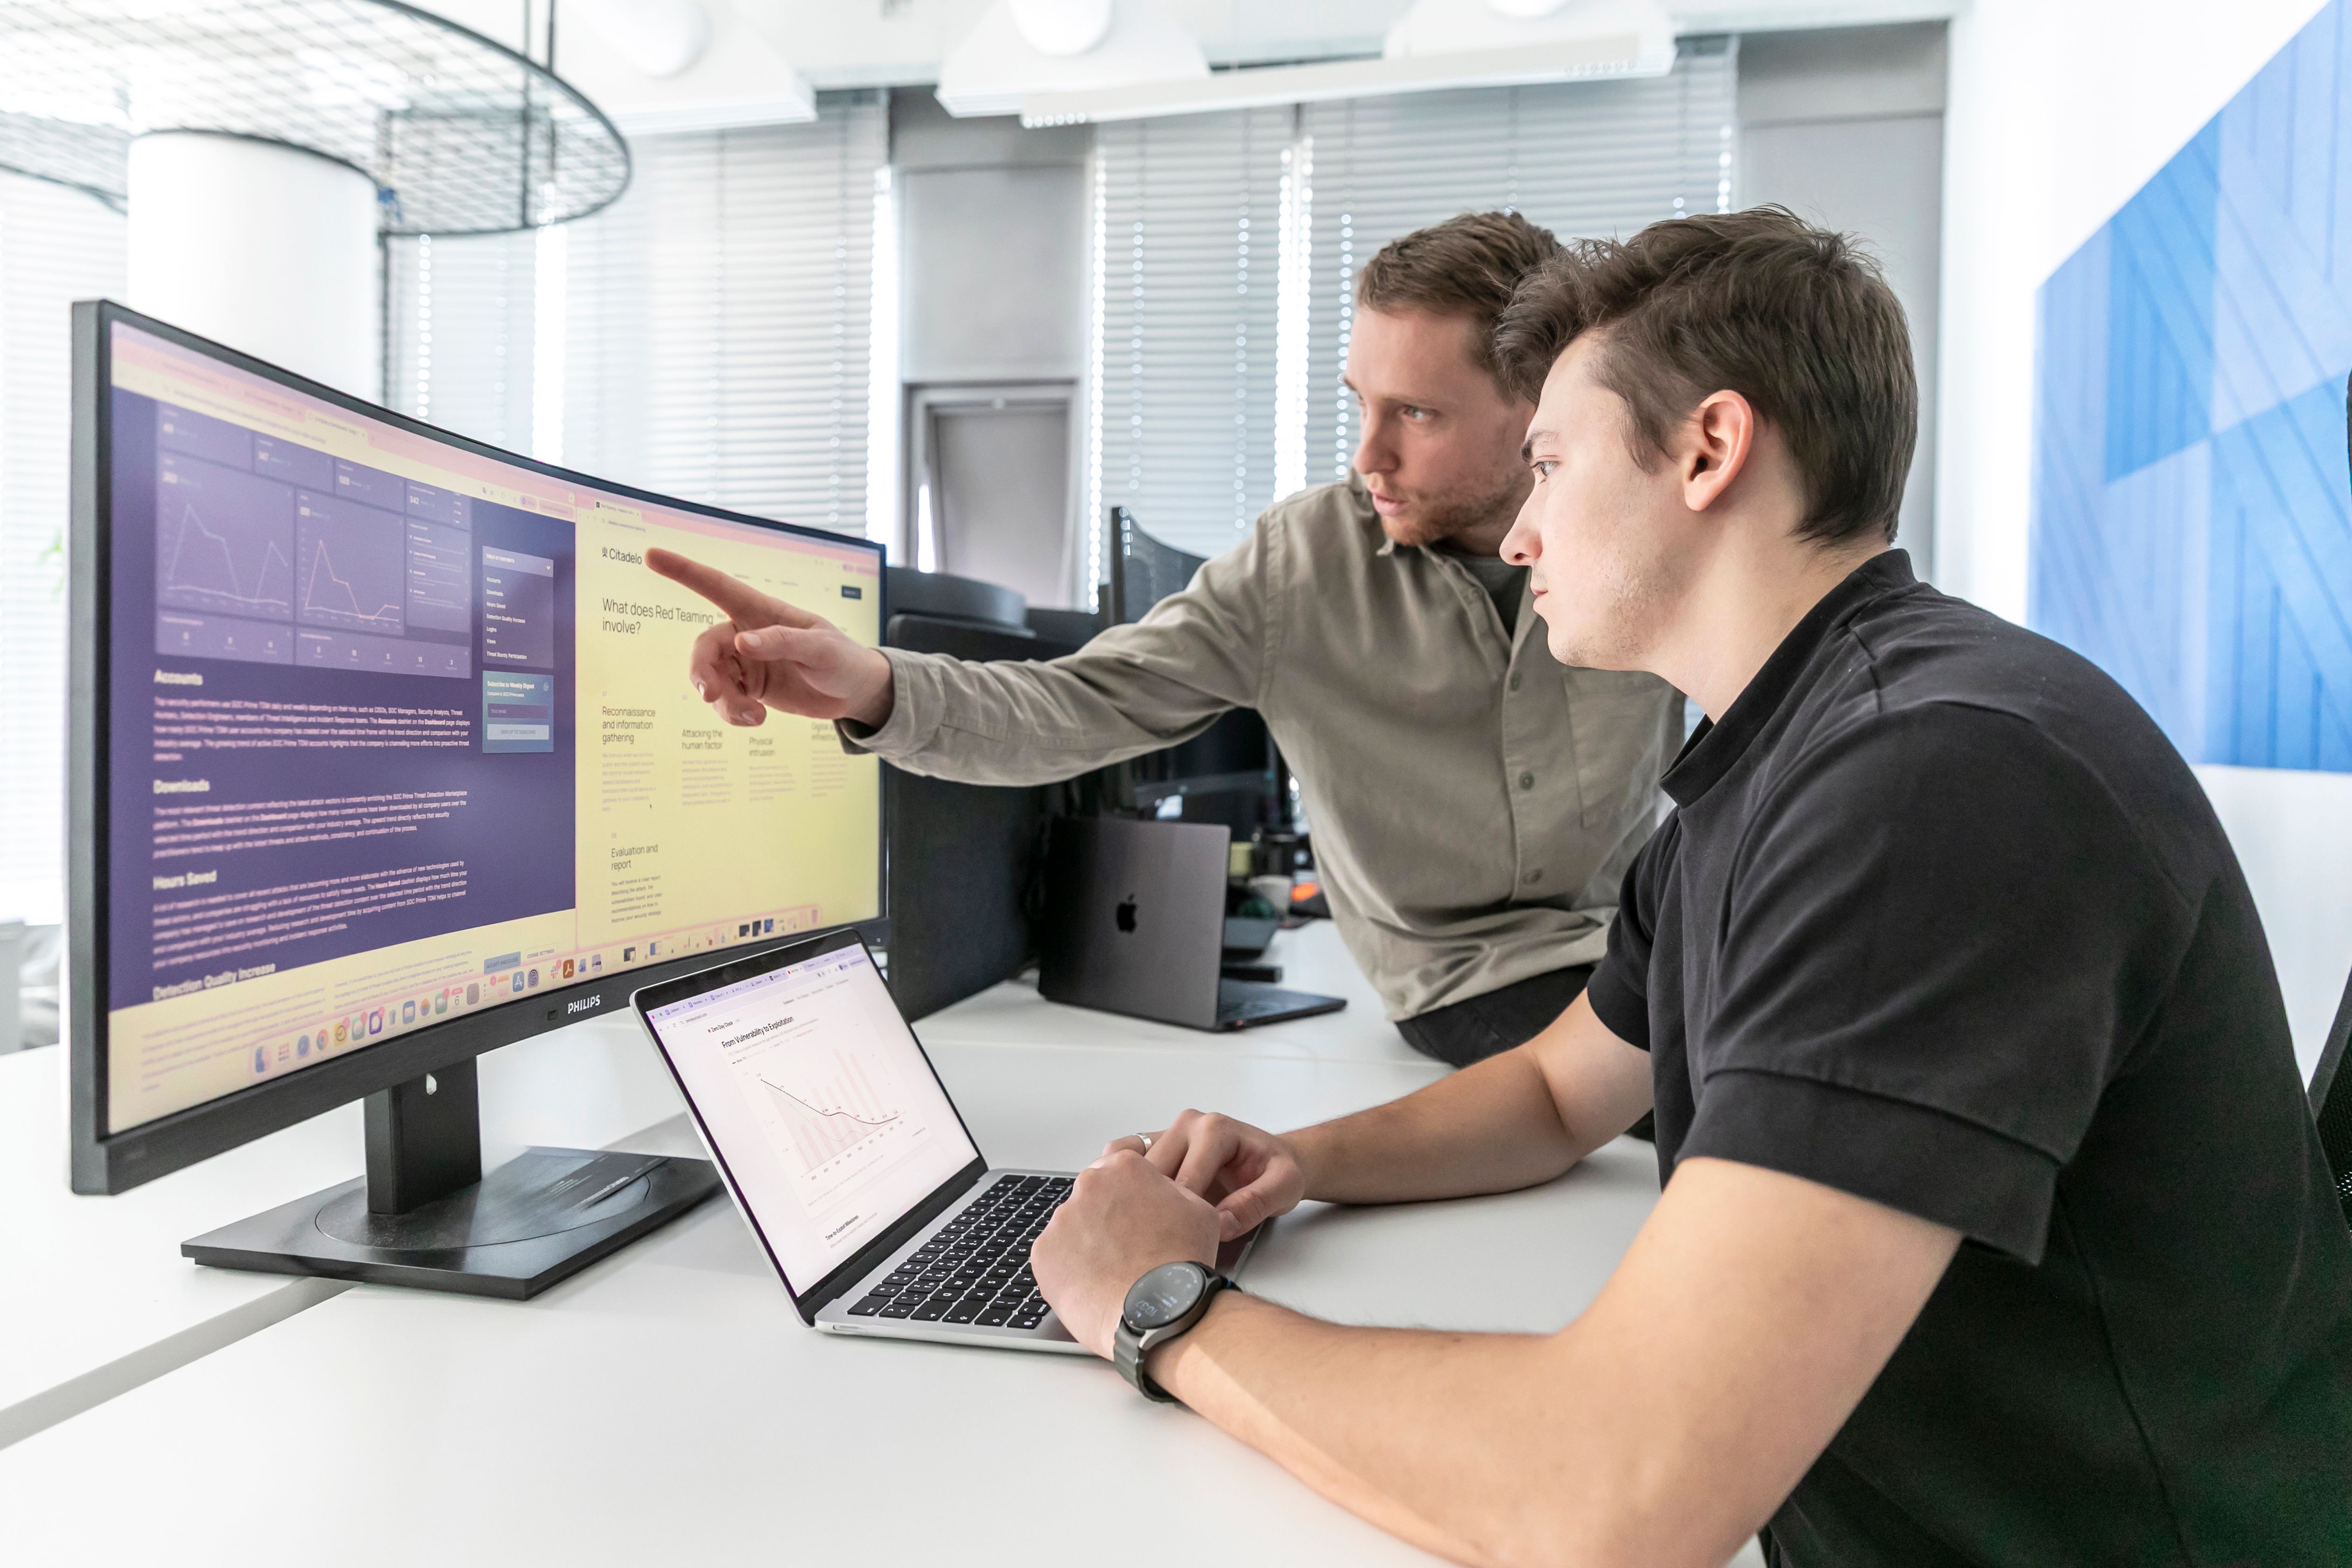
A cyberattack can have different consequences in each industry. In financial services, it may lead to an unauthorised payment. In healthcare, it can put sensitive data and patient safety at risk. In telecommunications, it may disrupt service availability, while in industry it can bring production to a halt. In a software company, a similar vulnerability may affect hundreds of customers through the supply chain. What matters is not only where a vulnerability is located, but also which systems, data and processes an attacker could affect by exploiting it.
When testing, we assess more than the technical severity of a vulnerability. We also consider potential financial losses, service outages, regulatory consequences, reputational damage and the impact on customers or business partners. By understanding your environment, we can determine the actual level of risk more accurately, set the right priorities and recommend measures that reflect how your organisation operates.
We also tailor security testing to the regulatory requirements of your industry, including NIS2, DORA, the Cyber Resilience Act, PCI DSS, EU MDR and IEC 62443. We explain the specific obligations and appropriate scope of testing in greater detail on the individual industry pages.