
News
17 September 2026
Security Audit vs. Penetration Test: What Is the Difference and When Do You Need Both?
An audit confirms that your security, procedures and responsibilities are properly defined. But is that enough? Real resilience cannot be assessed on paper alone. Only a penetration test can verify it in practice.
16 September 2026
Infrastructure penetration testing: why the internal network has become the epicentre of critical risks
71% of the infrastructure projects we tested contained at least one critical vulnerability. Most of these vulnerabilities were hidden in systems that companies considered secure simply because they were “not publicly accessible.

11 September 2026
How 628 Citadelo penetration tests revealed where your critical risks really lie
The greatest cybersecurity risk in 2026 is no longer limited to your internet-facing infrastructure. It is everything you already consider secure. In the first part of this series, we examine where critical risks are now emerging and what CISOs can do about them.
21 August 2026
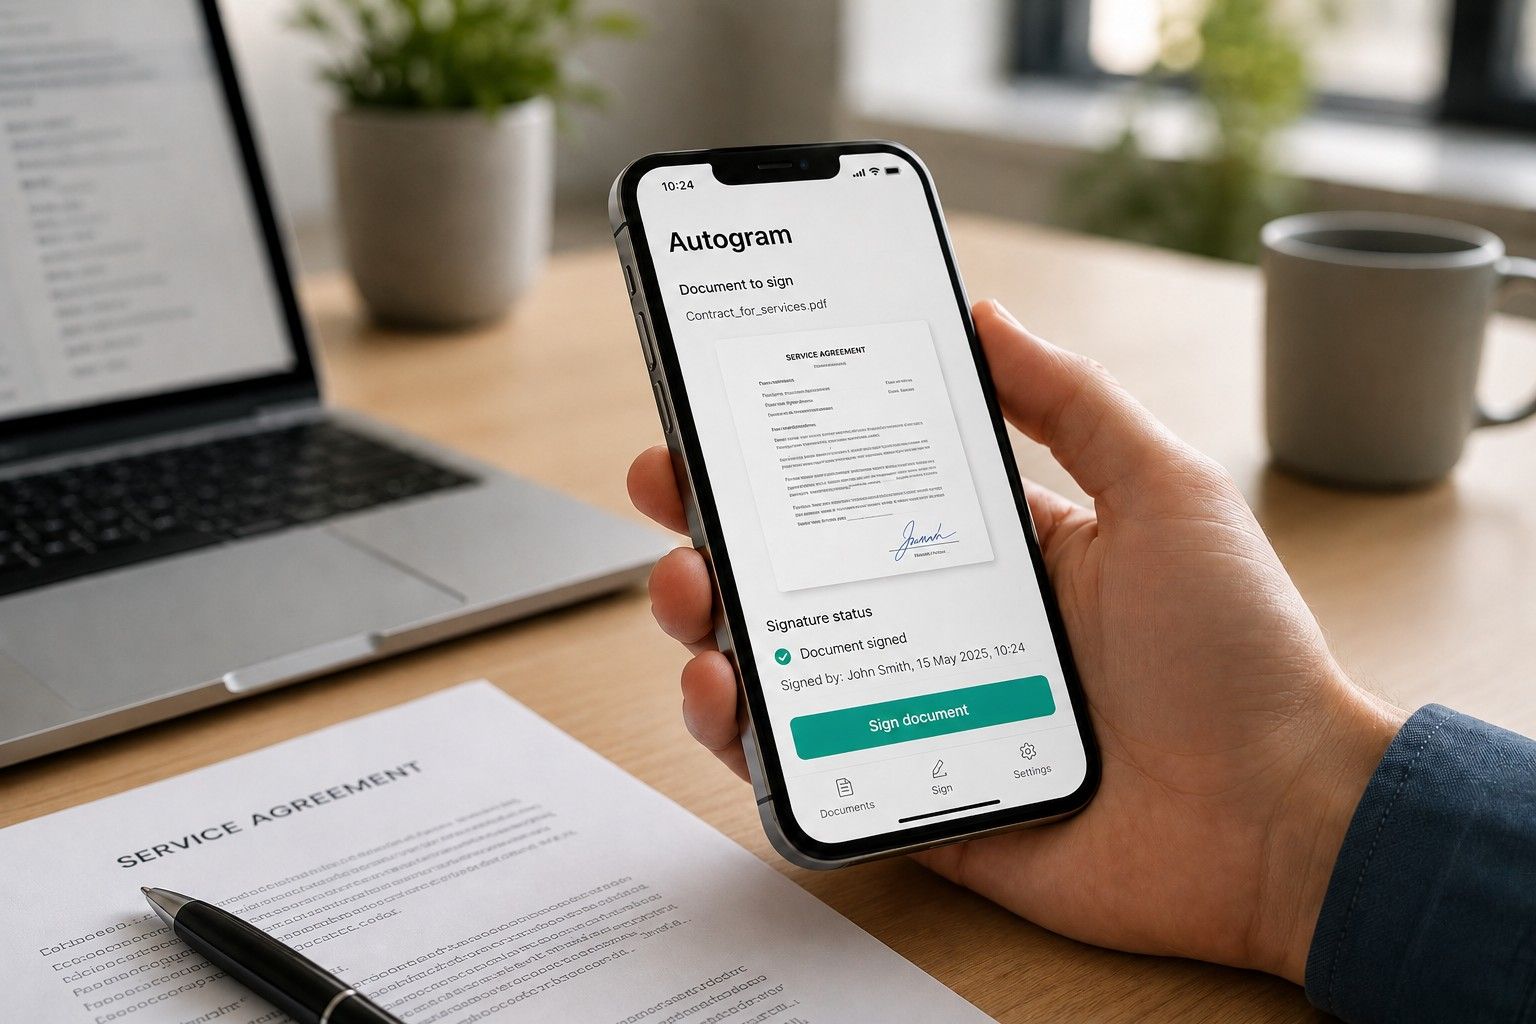
Penetration Testing of Autogram: What Remained in the App Used to Sign Documents in Slovakia
When an application is used to sign legally binding documents, its security is no minor detail. Slovensko.Digital knows this, which is why it had Autogram tested not only through a source code audit, but also through a real attack in the form of a penetration test.
17 August 2026
Cyber Resilience Act: the first deadline is not December 2027. It is 11 September 2026
For an actively exploited vulnerability, you have 24 hours to file the first report.
14 August 2026
The Cyber Resilience Act (CRA): who it applies to, what manufacturers must do, and by when
Product security used to be a commercial decision. The Cyber Resilience Act turns it into a condition for market access in the EU. Here is who the regulation covers, what it requires, which deadlines apply, and where to start.