
21 October 2026 / 3 minutes of reading
Red Teaming in Practice: How We Infiltrated an Organization Through Email and a Back Door
We sent employees an email impersonating their own CISO. Then, after business hours, we entered through a back door and connected to the internal network. This is the anatomy of one of our real-world Red Teaming engagements.
Red Teaming is the most realistic type of security testing we perform. Rather than focusing on a single system, it simulates the actions of a real attacker, combining technical attacks, social engineering, and physical intrusion. The results reflect this approach: across ten Red Teaming engagements, we identified critical or high-severity security weaknesses and failures in every single project. However, these engagements are not primarily about the number of findings. They are about understanding the entire attack chain.
Let's look at one of our projects from 2025. During the initial OSINT phase, we mapped employees and publicly accessible infrastructure. We immediately discovered our first opportunity: an email server without authentication that allowed us to send messages directly from the company's domain, without any warning indicating an external sender. Impersonating the organization's CISO, we sent several employees an email instructing them to install what appeared to be a mandatory security update. This gave us our first foothold in the internal network and domain.
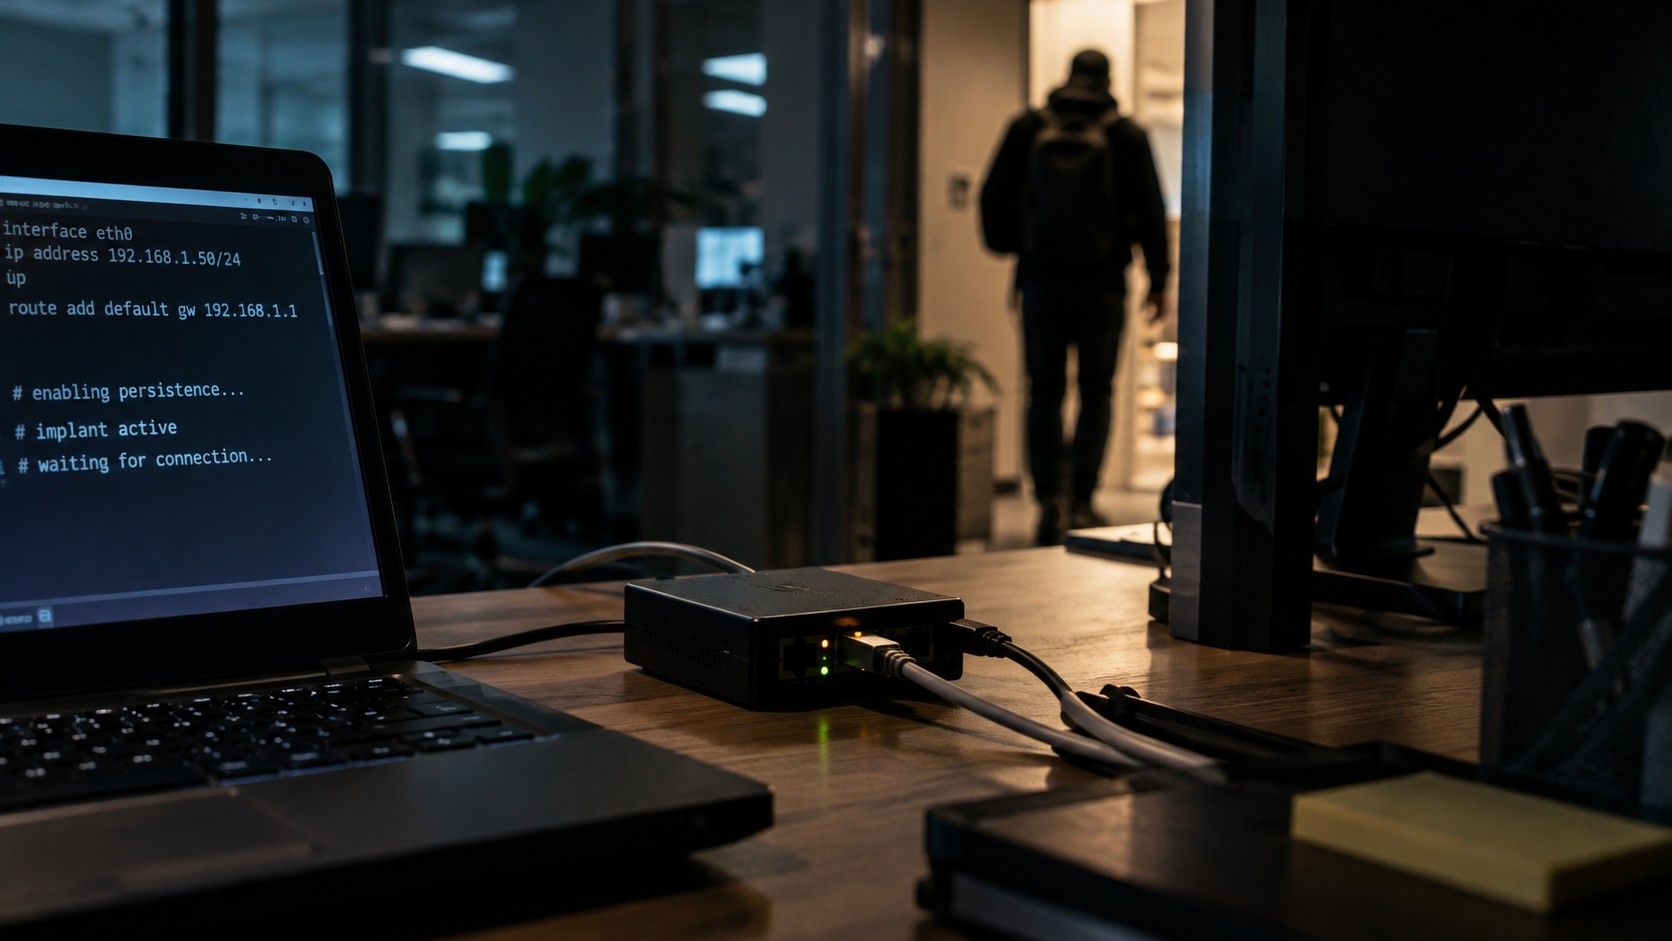
Our second way in was physical. Shortly after business hours, when the building was no longer guarded and the alarm had not been activated, we entered through a back door that was not covered by the physical security perimeter. We then discovered that the internal wired network required no authentication, allowing us to connect a small network device as an additional entry point. This network implant operated independently of the phishing attack and would remain usable even if the initial compromise was detected. If you're thinking that you would certainly notice such a device in your office, it may not be that simple. An implant like this is about the size of a phone charger. It can be hidden behind a monitor or inside a server rack, where nobody may look for it for weeks.
From there, the attack followed a scenario typical of internal infrastructure penetration testing:
- harvesting credentials from an unsecured network,
- escalating privileges by exploiting weaknesses in Active Directory,
- gradually gaining control over the entire domain.
Entering the building was not the most sophisticated part of the attack. It was simply the cheapest way to bypass all the security measures the organization had invested in. None of the individual weaknesses – a missing email server update, gaps in physical perimeter security, or an internal network without port-level protection – seemed particularly dramatic on its own. But when combined into a single attack scenario, they enabled the complete compromise of the organization. And it is precisely this chaining of weaknesses that testing individual systems alone cannot reveal.
What Does This Mean for CISOs?
Red Teaming answers a question that a conventional penetration test cannot fully address: how would my organization respond if an attacker combined multiple individual weaknesses into one coordinated attack?
Would Your Organization Withstand a Similar Attack?
Red Teaming assesses your organization's ability to withstand a realistic attack combining technical vulnerabilities, human factors, and physical intrusion. Identify security weaknesses before real attackers exploit them.
Other interesting articles
All news

Sign up for our newsletter for all the important cybersecurity and ethical hacking news.
© 2024 citadelo AG. All rights reserved.


