
27 October 2026 / 6 minutes of reading
Social Engineering and Vishing: Why Are Attacks on People Still So Successful?
Even if your spam filter caught 100% of phishing emails, attackers might still need only a single phone call using the cloned voice of a colleague or manager. But could you recognize a fraudulent message yourself? Find out in our short phishing quiz.
In 2025, we carried out four times as many social engineering projects as in 2024, and the results were clear. On average, attacks succeeded with 40% of the employees targeted, particularly during an organization’s first test. In other words, four out of every ten employees fell for the attack. More than half of the projects resulted in a critical security risk.
Despite advances in technology, email remains the most common attack vector, for a simple reason: attackers can send hundreds of messages and only need one person to click. A single successful click can be enough. Depending on who falls for the attack, the consequences can be devastating. The 2024 Arup incident, in which an employee transferred approximately $25 million following a video call with AI-generated impersonations of colleagues, is one of the most striking examples of this kind of attack.
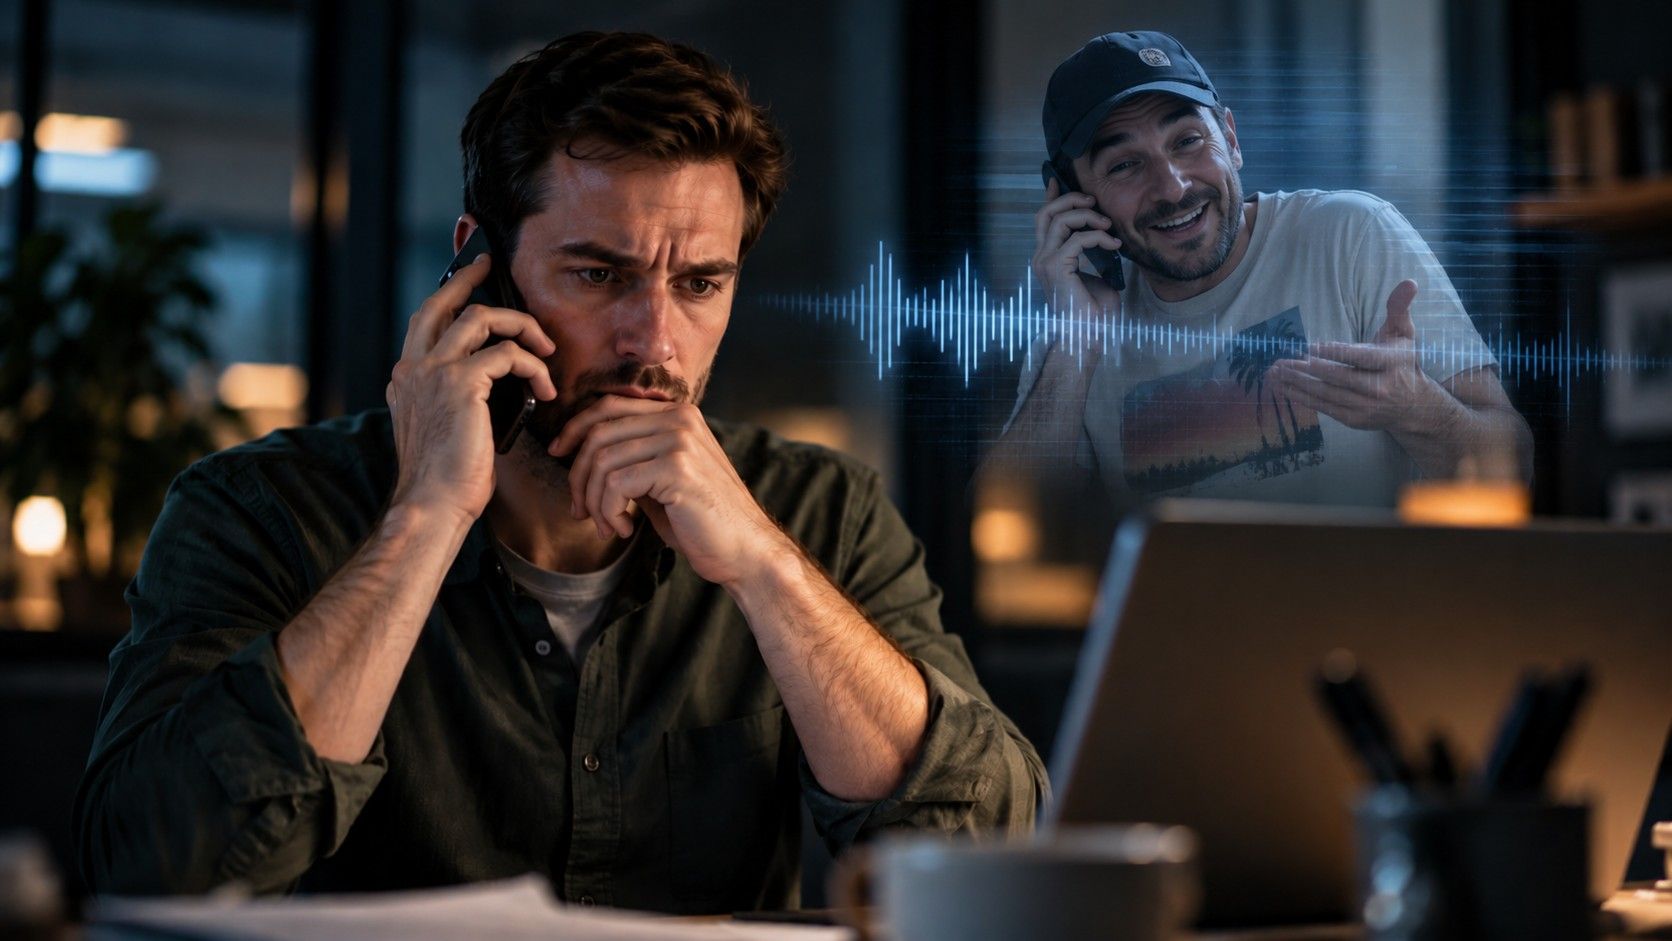
But imagine a best-case scenario in which your spam filter and firewall work perfectly, blocking every malicious email. Not a single phishing message reaches an employee's inbox. We could still find a way in. All we need to do is call your employees from a spoofed number and clone the voice of someone they trust, such as their manager or a senior executive, in real time. Getting a voice sample is surprisingly easy. A few minutes of audio is enough, and many executives freely provide that material through conference talks, podcasts and short videos on social media. Even if someone has no public recordings, a single pretext call disguised as a customer satisfaction survey or a sales pitch can give us the few seconds of audio we need.
This is not a hypothetical scenario. In 2025, a large-scale vishing campaign targeting IT help desks and single sign-on (SSO) systems affected more than 100 organizations. The campaign has been linked to groups including Scattered Spider and ShinyHunters. The employee answering the phone hears a familiar voice making an urgent request. The security controls the company has invested in may never even come into play. This is why comprehensive Red Teaming exercises assess not only technical vulnerabilities but also the ways attackers can exploit human behaviour.
Our data also tells a more encouraging story. In organizations that regularly train and test their employees, attack success rates fall from around 40% to single digits. Human risk is not fixed. It can be reduced through continuous testing, measurement and improvement.
What Does This Mean for CISOs?
If your organization has never conducted a social engineering assessment, you should be prepared for an attacker to succeed against roughly 40% of your employees. That is why identity verification matters just as much over the phone as it does over email. Never reset a password or an MFA factor based solely on a phone call. Any urgent request involving a payment or a change to access permissions should require a second, independent verification step, such as calling back on a number already on record or confirming the request through another trusted channel. This applies regardless of whose voice you think you hear.
Would Your Employees Recognize a Real Attack?
Phishing, vishing and identity impersonation can bypass even sophisticated technical security controls. Put your employees' resilience to social engineering to the test and uncover weaknesses before attackers exploit them.
Other interesting articles
All news

Sign up for our newsletter for all the important cybersecurity and ethical hacking news.
© 2026 citadelo AG. All rights reserved.


