
19 November 2026 / 6 minutes of reading
Hackers Defrosted Supermarkets. Is Your Company Next?
Attackers remotely changed the settings of refrigeration systems in European supermarkets. The incident shows how a forgotten administration interface or poorly protected supplier access can put operations, applications and sensitive data at risk.
In early November 2026, attackers remotely changed the temperature settings of refrigeration systems in European supermarkets. But the incident is not just a warning for retailers. The same problem can affect a bank, hospital, technology company or industrial business if the organisation is unaware of an internet-facing system or fails to control its suppliers’ remote access.
When people hear about a cyberattack against a supermarket, they usually imagine disabled checkout systems, encrypted servers or stolen payment data. In early November 2026, however, European stores faced an attack on technology essential to their daily operations: refrigeration systems.
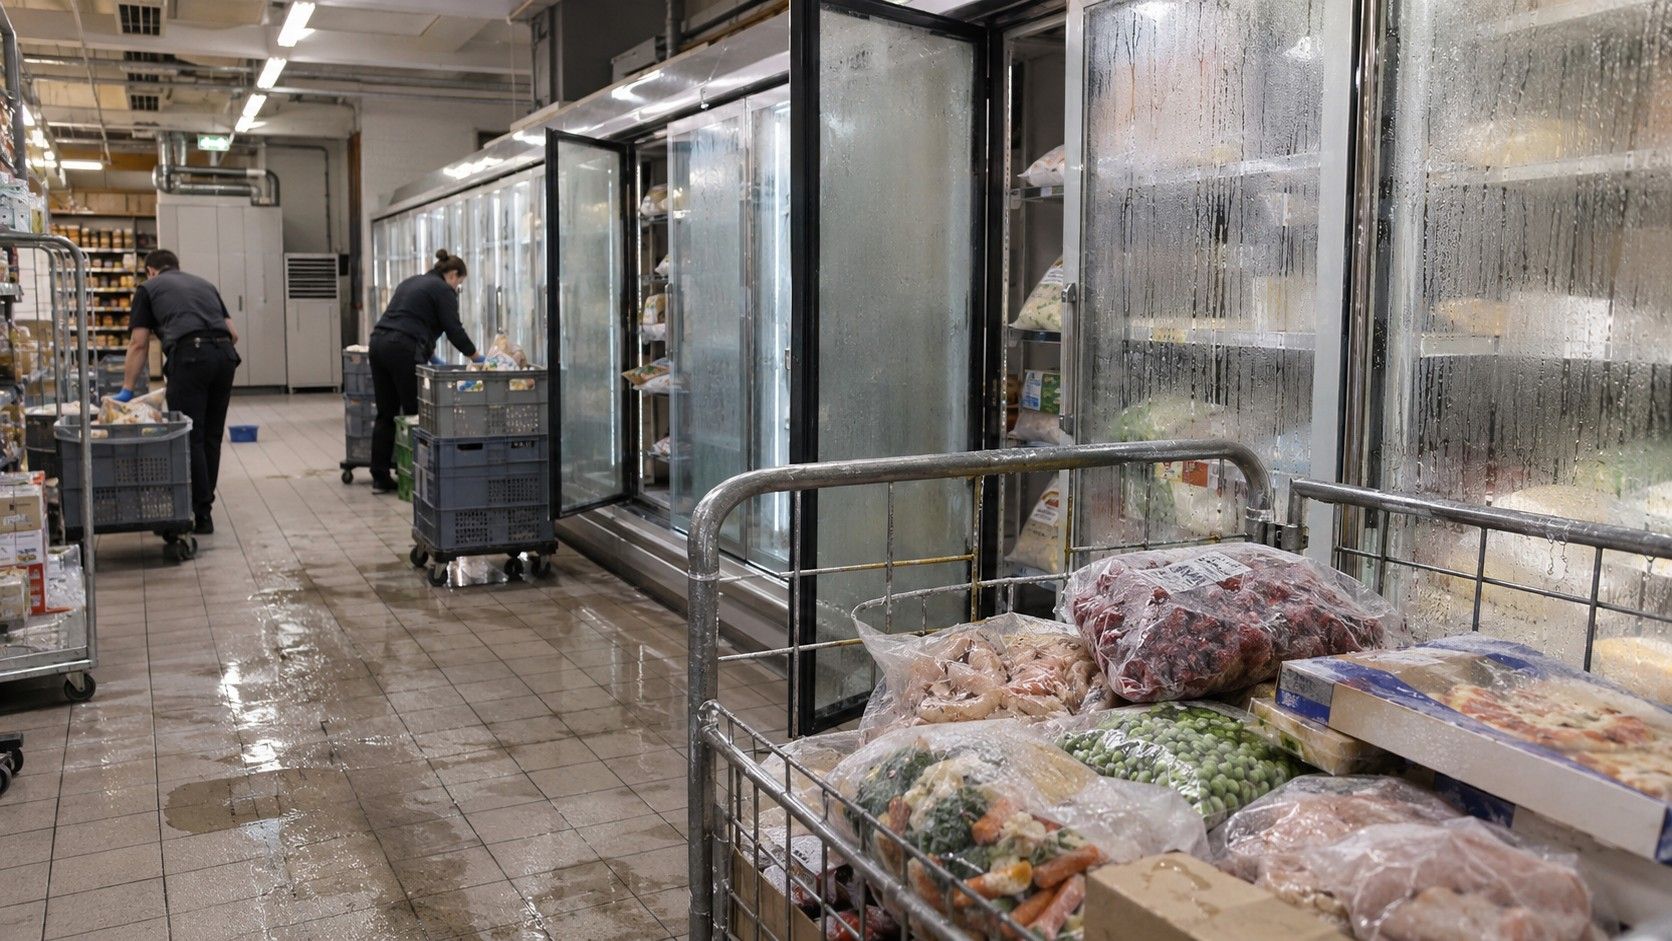
The first major wave affected hundreds of French supermarkets on 11 October. A second followed during the night of 2 November, targeting stores in Belgium, the Netherlands, Sweden, Ireland, Estonia and other European countries. Attackers remotely accessed refrigeration controls, changed temperature settings and activated defrost cycles outside their scheduled times. The result was spoiled food, operational disruption and significant financial losses.
Routine maintenance became an entry point for attackers
Modern refrigeration systems are no longer isolated devices controlled solely by buttons on a wall. Their control units allow operators to monitor temperatures, change settings, schedule defrost cycles, receive alerts and manage multiple locations remotely. This makes maintenance easier, but it also creates another interface that must be properly secured.
Some of the affected systems had administrative interfaces exposed directly to the public internet. Before the attacks, Censys had identified approximately 6,700 publicly accessible systems across two monitored groups of refrigeration equipment. Attackers could discover them through automated scanning, identify the devices and then try a default password, known vulnerability or authentication flaw.
The exact method used to gain access at individual stores has not yet been publicly confirmed. However, some Danfoss controllers were affected by CVE-2025-41450, a vulnerability that made it possible to derive administrator credentials from the current date. When combined with another vulnerability, attackers could remotely execute commands on the device. Six previously unknown flaws were later disclosed that could allow certain firmware versions to be compromised without valid credentials. There is no evidence, however, that these vulnerabilities were used in every attack.
Once access had been gained, the attackers no longer needed sophisticated malware. They used legitimate system functions and changed parameters that should have been accessible only to administrators or service technicians. The equipment then carried out exactly what its control unit instructed it to do.
The same problem can affect any industry
Supermarkets experienced the impact through spoiled food. In other organisations, compromising a publicly accessible system may have very different consequences.
In a bank, the target could be a supplier’s remote connection, an ATM, an application administration interface, a physical access system or equipment in a data room. In a hospital or MedTech company, attackers may look for a path through a connected medical device, service account, cloud platform or system storing patient data. In an industrial facility, they could disrupt a production line, warehouse, energy system or building management platform. A technology company may have an exposed testing environment, development tool, cloud console or forgotten administration interface.
The technologies and consequences vary, but the underlying security problem remains the same: an organisation cannot protect a system it does not know about or an access route it does not control.
Large companies use hundreds of domains, public IP addresses, cloud services, applications, devices and external partner accounts. Some were created for testing, others are managed by suppliers, and some remained accessible after infrastructure changes. The security team may not have a complete overview of technologies operated by another department or an external service provider.
Attackers do not care whether a system belongs to the IT department, developers, facilities management or a medical device supplier. They look for the easiest way in.
A stronger password does not solve the entire problem
The first response to an incident like this is often to change passwords and update the firmware. Both measures are necessary, but they may not eliminate the underlying risk: the administrative interface remains accessible to anyone on the internet.
Following the refrigeration system attacks, Ireland’s National Cyber Security Centre recommended removing direct access from the public internet. If remote administration is essential, it should be provided through a secure VPN or another protected solution. The authority also warned that applying updates, changing default passwords or enabling a stricter session mode may not be enough to protect an internet-facing device.
Companies should know which systems are externally accessible, who manages them and what permissions internal users and external partners have. Operational and connected devices should be separated from other parts of the network, while suspicious logins and configuration changes should trigger alerts. Unsupported devices should be isolated or replaced.
Suppliers must also be assessed. External companies often manage air-conditioning systems, medical technology, CCTV and access control systems, cloud platforms or network infrastructure. Their accounts may provide a legitimate yet privileged route into a customer’s environment. If one service account can access several systems or locations, compromising it may extend the impact far beyond a single device.
Documentation cannot tell you what an attacker can actually achieve
An organisation’s documentation may state that remote interfaces are not publicly accessible, supplier accounts have limited permissions and individual network segments are separated. But this does not prove that these protections work in practice.
Penetration testing can uncover forgotten public services, outdated devices, poorly secured remote access and possible attack paths following the compromise of a single account or system. Testers can determine whether an exposed interface could provide access to sensitive data, internal applications, operational technology or other parts of the network.
The result should not be just a list of technical vulnerabilities. The company needs an answer to a practical question: what could an attacker achieve after compromising the organisation’s weakest system?
Do you know what attackers can access in your organisation?
A forgotten administration interface, outdated device or overly broad supplier access can open the way to applications, operational systems and sensitive data.
Citadelo will assess your external attack surface, remote access controls and the real attack paths leading into other parts of your organisation.
Other interesting articles
All news

Sign up for our newsletter for all the important cybersecurity and ethical hacking news.
© 2026 citadelo AG. All rights reserved.


