
30 October 2026 / 4 minutes of reading
TECHBOARD #4: Attackers Push Malicious LiteLLM Update, Critical Ruby Flaw Threatens GitLab
Attackers slipped malware into the official LiteLLM distribution, while a critical GitLab flaw could allow unauthenticated remote code execution. TECHBOARD #4 also covers a certificate authority using a private key valued at just 4, new PHP2Shell complications, and other security findings.
Real world hacks
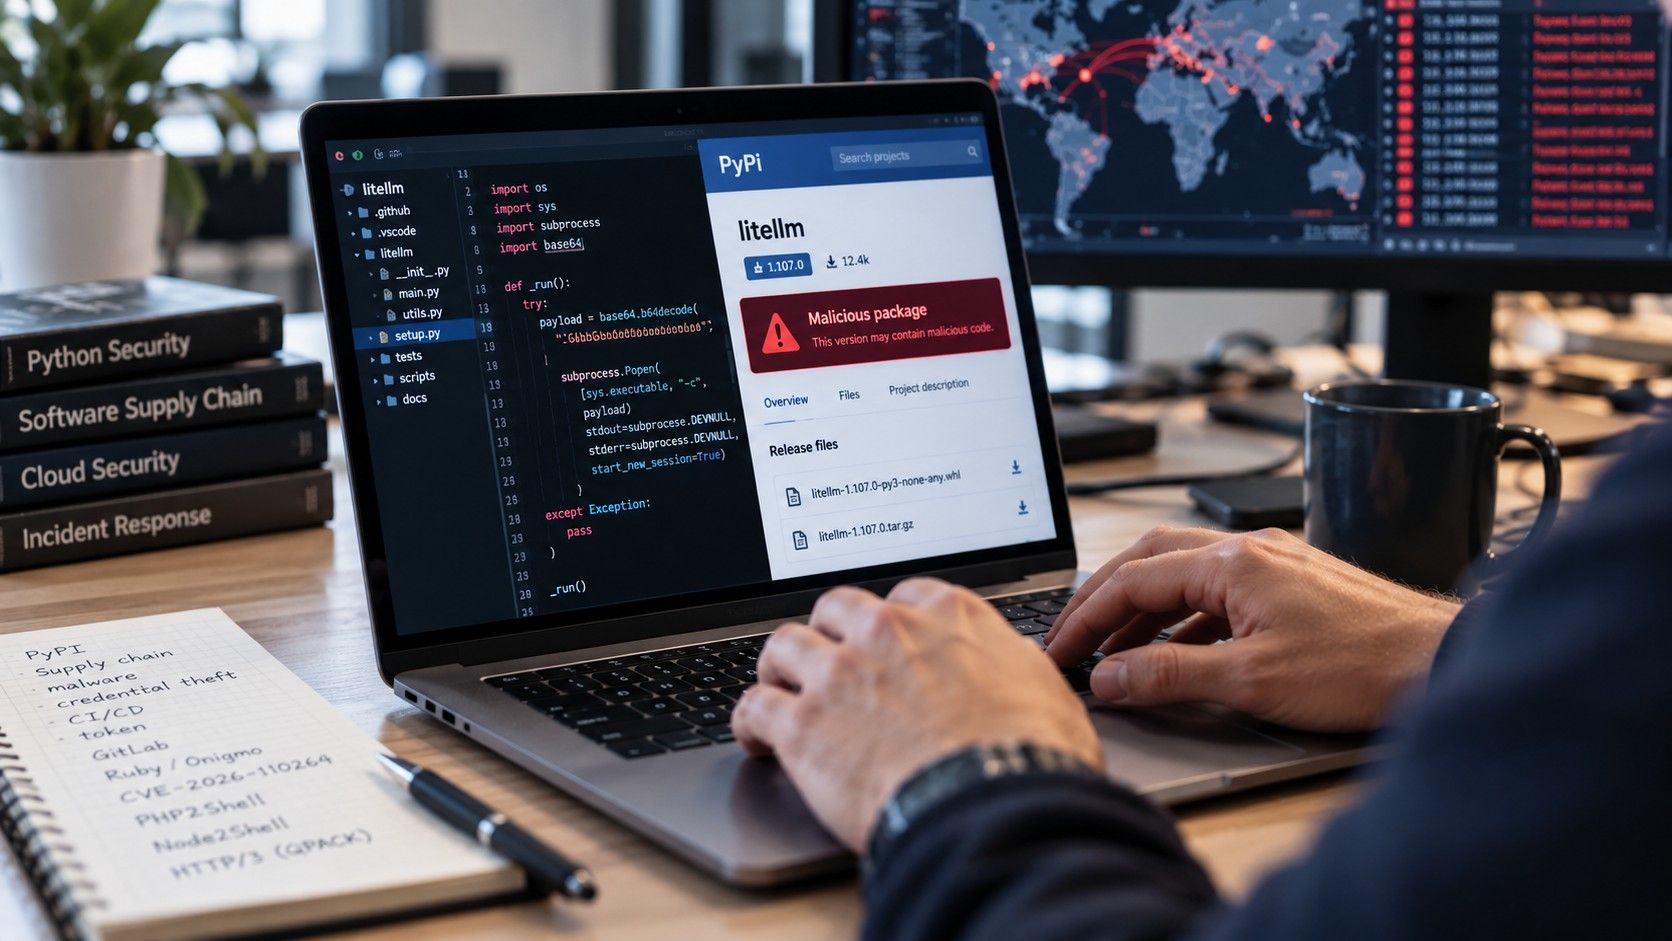
Attackers compromised the official LiteLLM distribution and delivered credential-stealing malware to users. Malicious version 1.107.0 was available on PyPI for approximately two hours on October 21 and remained accessible through container registries for several more hours. The malware collected credentials, cloud tokens, and other secrets. It could execute during Python initialization, even without importing the LiteLLM library. According to the official incident analysis, the attack began back in May, when developers accidentally exposed an access key and failed to revoke it. In October, the attacker used that key to obtain privileged GitHub tokens, modify a CI/CD workflow, and publish signed malicious packages. A single unrevoked key was enough to compromise the software supply chain.
Czech Technical University in Prague (CTU) suffered a cyberattack that prompted the precautionary shutdown of several systems. On October 22, the university reported that the active attack had been stopped and that infrastructure recovery was underway. The incident occurred amid widespread attempts to exploit critical PHP vulnerabilities. However, successful exploitation of PHP2Shell in this particular attack has not been confirmed.
Vulnerability landscape
A critical GitLab vulnerability with a CVSS score of 10.0 could allow unauthenticated remote code execution under certain conditions. CVE-2026-110264 affects the processing of regular expressions in Onigmo, the regex engine used by Ruby. A specially crafted expression containing a large number of repetitions can cause internal identifier overflows and memory corruption. Notably, GitLab also uses regular expressions when processing user input and CI/CD configurations. Attackers therefore do not need to target authentication directly; they can exploit a low-level component that processes untrusted data. Ruby developers subsequently fixed four related vulnerabilities in Onigmo. GitLab released security updates and two detection mechanisms focused on crashes involving Onigmo and unusual content-rendering errors. The case highlights how potentially critical vulnerabilities can be hidden in libraries used to process seemingly harmless input.
Certificate authority eMudhra used cryptographic private keys so weak that one had a value of just 4. Eight intermediate certificate authorities had private keys with values below 256, making it possible to derive them almost instantly from their public certificates. Six of these authorities could issue TLS certificates, while the other two could sign code. An attacker possessing such a key could potentially issue fraudulent certificates that vulnerable systems would consider trustworthy. eMudhra acknowledged a flaw in its key-generation script and revoked the affected authorities. No confirmed exploitation has been reported. The response continued on October 26, when Microsoft issued an out-of-band update to remove additional certificates associated with the affected hierarchies from the Windows trusted certificate store.
PHP2Shell continues to cause problems for administrators, with new issues emerging even after patching. On October 26, CISA added the critical vulnerabilities to its Known Exploited Vulnerabilities catalog. Meanwhile, a regression in the patched PHP versions 8.4.27 and 8.5.12 can cause applications using SimpleXML to crash. This regression is not directly related to the PHP2Shell fixes. Tenable provides an up-to-date overview. We also explain how to assess the security of your infrastructure in our article on critical PHP vulnerabilities.
The Node2Shell vulnerability allows attackers to execute code through maliciously crafted data compressed using Brotli. CVE-2026-111497 causes an out-of-bounds memory write. Imperva researchers successfully demonstrated remote code execution in a vulnerable version of Node.js. Patched versions are available.
A small HTTP/3 request can exhaust the memory of a vulnerable server. FoxIO researchers discovered a way to exploit QPACK header compression that causes servers to allocate many times more memory than the amount of data they receive. Seven out of ten implementations tested were vulnerable.
CITADELO news
Social engineering attacks succeed against 40% of employees tested. In our new article on phishing and vishing, we explain why a single phone call using a manager's cloned voice can be enough to deceive employees and how regular testing helps reduce attack success rates.
Do you know what vulnerabilities are hiding in your infrastructure?
Critical security flaws can exist even in widely used libraries and tools. Citadelo's penetration testing services help identify weaknesses in your systems before attackers can exploit them.
Other interesting articles
All news

Sign up for our newsletter for all the important cybersecurity and ethical hacking news.
© 2026 citadelo AG. All rights reserved.


