
28 October 2026 / 12 minutes of reading
Red Teaming vs. Penetration Testing: Key Differences and Benefits
What's the difference between penetration testing and red teaming? Learn what each approach reveals, their key benefits, and when combining them can strengthen your organisation's cybersecurity.
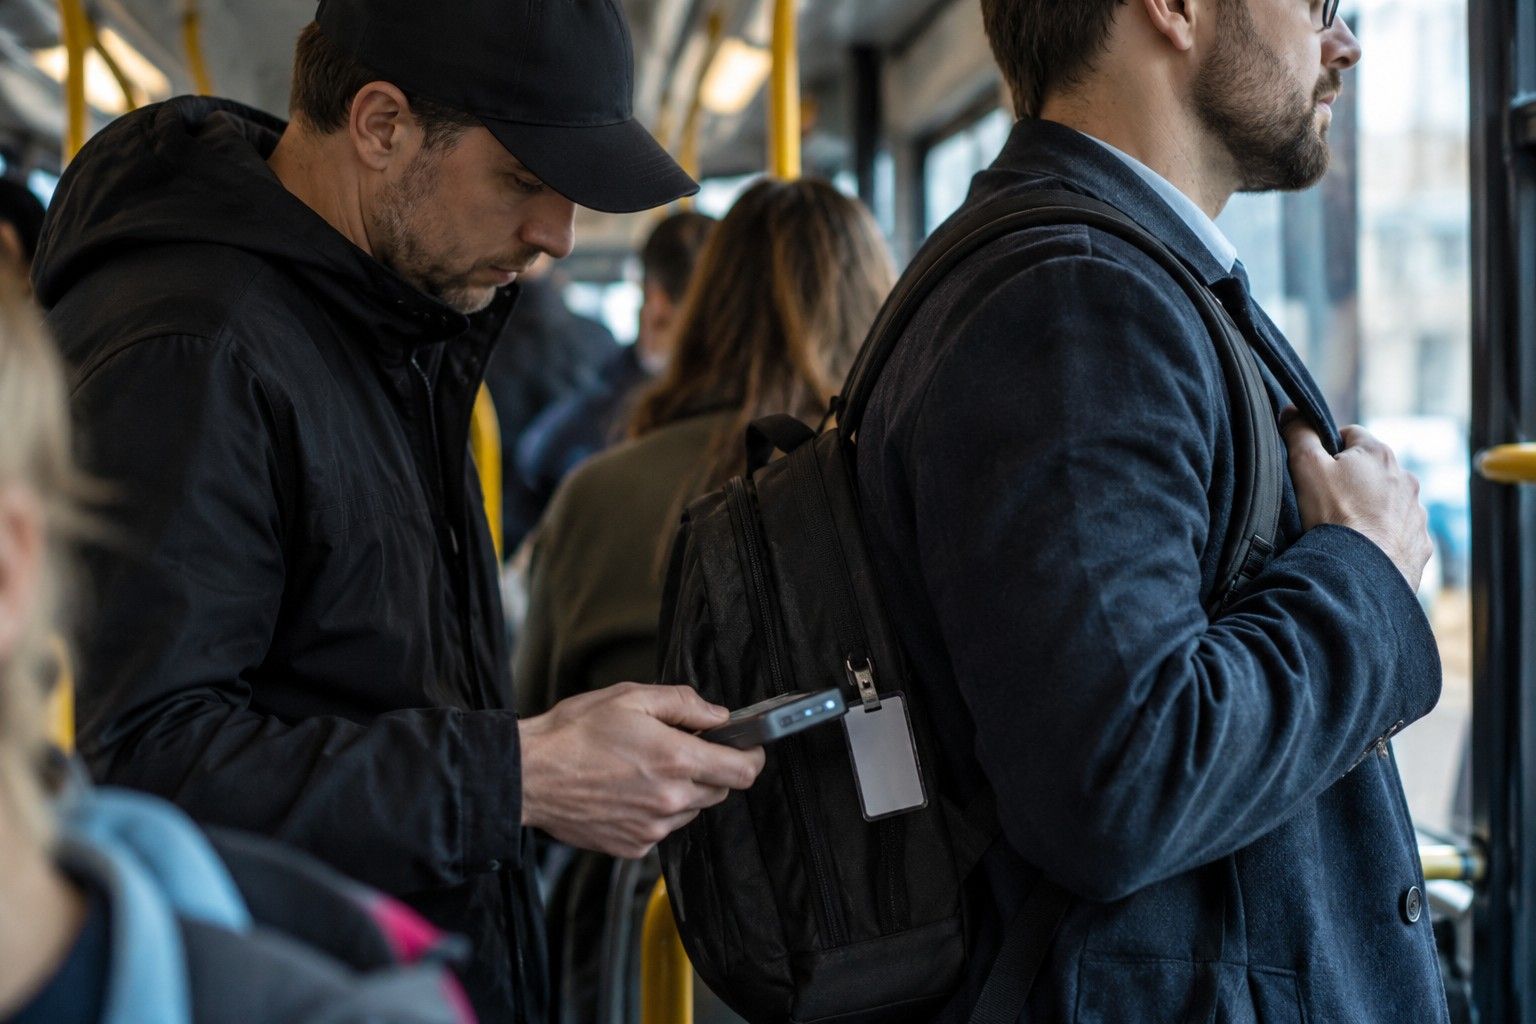
An employee of Company XYZ is travelling on a crowded bus, unaware that the person standing next to him is using a special device to read the data from his workplace access card. The employee never even takes the card out of his hand. The following morning, someone uses a cloned card to pass through the company's security turnstile. Even though the original card has already been used that day, the access control system raises no alarm. Sounds like a scene from the Jason Bourne trilogy? Yes and no. The techniques might seem straight out of a movie, but this really happened, and the people behind it were members of our red team.
The cloned card got us exactly where we needed to be. In buildings with shared access control systems, access cards often have broader permissions than the company realises. That's why it's important to review physical access permissions and monitor access logs for unusual activity.
Once inside, we left a small flowerpot on an office windowsill. It stayed there for an entire week without anyone asking who it belonged to. Employees had no idea that a computer was hidden inside the flowerpot's false bottom. Connected to the internet via a mobile network, it allowed us to continue testing the wireless network long after our team had left the building.
After a week of maintaining a virtual presence inside the building, we stopped trying to stay under the radar. We scanned available networks, attacked the internal Wi-Fi and used guest access to explore several network segments. We were doing exactly the kind of things that should have triggered every security alarm. Yet there was no observable response. The company had security tools in place, but our exercise showed they weren't working as intended.
Penetration Testing vs. Red Teaming: The Key Differences
This story comes from one of our own red teaming engagements, a practical approach to assessing an organisation's security. Although red teaming and penetration testing are often confused, they assess security in different ways. Penetration testing identifies exploitable vulnerabilities in a specific system, while red teaming follows an attacker's path towards a critical objective and examines how the organisation responds.
Penetration testing typically takes a broad approach within an agreed scope, examining an application, for example, from multiple angles. Red teaming, on the other hand, focuses on reaching a clearly defined objective, usually testing the organisation's defensive response along the way. The difference lies not only in the scope of the engagement, but above all in the results the organisation needs. In this article, we'll compare the benefits of both approaches and help you decide which is right for your business.
Penetration Testing: From Vulnerability Discovery to Verified Remediation
Penetration testing, or pentesting, assesses an agreed application, system or part of an organisation's infrastructure. Testers identify vulnerabilities that can actually be exploited, evaluate their potential impact and recommend how to address them. For a customer portal, this might mean checking whether an ordinary user can access someone else's invoice or administrative functions. In an internal network, testers might look for unpatched services or exposed devices.
Developers and administrators receive verified findings, information about their impact and recommendations for remediation. They can then prioritise risks, implement fixes and use retesting to confirm that the issues have been resolved. One of the main strengths of penetration testing is its systematic coverage of the agreed scope. It can involve considerable technical depth and demonstrate how several vulnerabilities could be chained together in a single attack.
If a company has already undergone a security audit, a penetration test can provide practical verification of selected security controls. We explain the distinction in more detail in our article on security audits vs. penetration testing.
Need to know what to fix before launching a system or after making significant changes?
Red Teaming: Simulating Attacks and Testing Your Response
Red teaming starts with an objective that matters to the business. For example, an exercise might assess whether an attacker could gain access to sensitive information or disrupt a critical business process. Working within agreed rules of engagement, the team looks for a realistic path to that objective, combining technology, people and processes. Depending on the scenario, this may also involve testing physical security, just as we did in the opening story. Social engineering has long been part of red teaming, and phishing remains a common way to test employees' security awareness.
At the end of the exercise, the organisation receives a documented attack path and an assessment of its preventive controls, detection capabilities and response. When the defensive team is involved, the exercise can also measure when suspicious activity was detected, how it was escalated and what actions were taken to contain it. The findings help identify which procedures and security measures need improvement. A follow-up exercise can then verify whether those changes have worked. Our story involving the cloned access card and the computer hidden in a flowerpot, for example, also highlighted weaknesses in physical access controls, an area that can easily fall outside the traditional scope of IT security.
What Red Teaming Doesn't Cover
Red teaming doesn't necessarily examine every application encountered along the path to its objective in detail. If you need a thorough assessment of a customer portal, a dedicated penetration test is the better choice. Both services operate within an agreed scope, with clearly defined permitted activities and safeguards to minimise disruption to business operations. You can learn more in our overview of Citadelo's red teaming services.
Penetration Testing vs. Red Teaming: A Simple Comparison
Which Approach Is Right for Your Organisation?
For CISOs and business leaders, the key question is what decision the assessment needs to support. Approving the launch of an application and prioritising security fixes requires a different approach from determining whether the organisation can withstand a coordinated attack against a critical business process.
Penetration testing is the right choice when applications, access permissions or infrastructure are changing and you need specific findings to guide remediation. It's also valuable when making changes to cloud environments. However, if you want to know whether your defensive team can recognise and handle an incident across the organisation, penetration testing alone won't fully answer that question.
Red teaming is the right choice when you want to assess how well a critical asset or business process is protected against a complex attack. It's particularly valuable when security tools, procedures and response teams are already in place, but management doesn't know how effectively they work together. If your immediate priority is to identify and eliminate unknown vulnerabilities in a specific application, a targeted penetration test will provide more actionable findings.
Want to know whether your team can detect an attack in time and respond effectively?
A Comparison for CISOs
How Can Penetration Testing and Red Teaming Work Together?
An organisation's size alone doesn't determine which approach is appropriate. What matters is the value of the business process being protected, the maturity of existing security controls and the organisation's ability to turn findings into meaningful improvements. Penetration testing can lay the groundwork for a broader red teaming exercise. Conversely, red teaming may uncover a system that warrants a more detailed penetration test. For management, it's important to assign clear responsibility for remediation. When testing incident response capabilities, organisations should also measure time to detection, escalation and containment.
Not Sure Whether Your Organisation Needs Penetration Testing or Red Teaming?
Every organisation faces different cybersecurity risks. During a free 15-minute consultation, our experts will help you determine which type of security testing best meets your needs and how to assess your systems' resilience against real-world cyberattacks.
Other interesting articles
All news

Sign up for our newsletter for all the important cybersecurity and ethical hacking news.
© 2026 citadelo AG. All rights reserved.


